
The installed 1xBet app on your phone works nothing like the browser version – cached pages, persistent login and dedicated push alerts replace the reload-and-log-in cycle a mobile site forces on you each session.
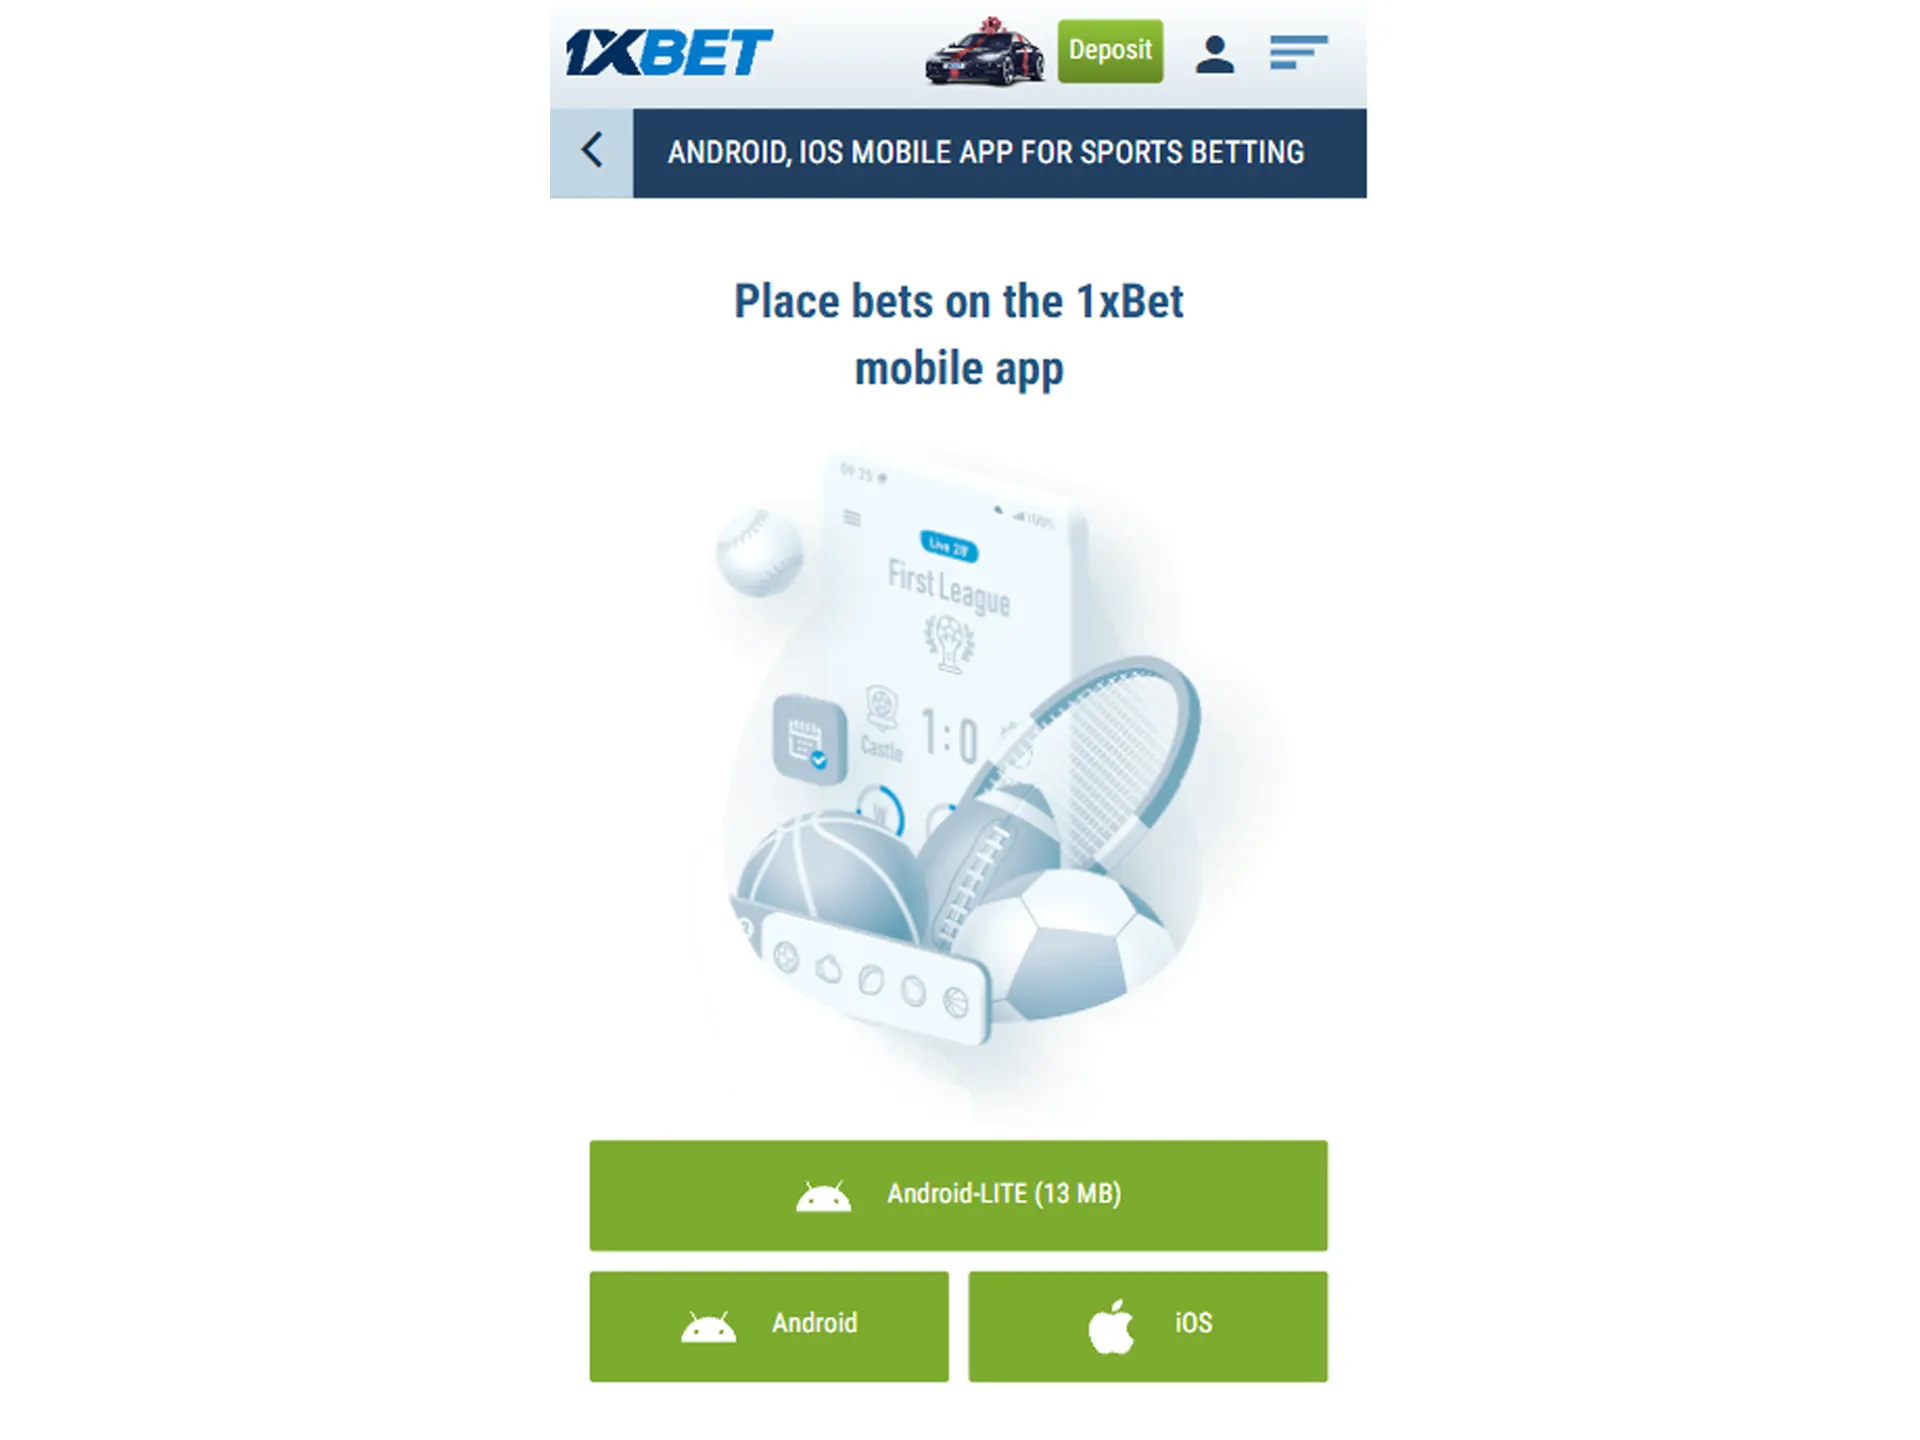
That convenience only pays off when the APK file you’re about to run actually came from the operator and not from a repackaging site, so the sensible move is treating the whole process as a small security check rather than a settings chore.
This guide walks through that check in the order Android itself presents it: source first, download second, permission third, then the features, updates and error messages waiting on the other side.
Separating Trustworthy Mirrors From Repackaged Files
Search results for betting APKs mix official distribution pages with aggregator portals that re-upload files under their own names, and the difference decides whether your phone receives a genuine build or a modified one. A trustworthy page loads over HTTPS, carries the operator’s own branding, lists the version it serves, and never wraps the file inside a downloader executable. Aggregator pages often pad the description with keywords and bundle an installer that fetches the APK through an ad-filled redirect chain.
Practical signals worth checking before you tap anything:
- The domain belongs to the operator or a clearly linked regional partner, not a generic “apk-download” farm.
- The page names the app version and publishes its own support channel instead of borrowed screenshots.
- The file downloads directly as an .apk once you tap, without an intermediary “download manager” prompt.
- The page offers a checksum or at least a file-size figure you can compare after download.
None of these checks guarantees authenticity on its own – they stack into a reasonable judgement. When in doubt, stop and switch to the mobile website, which needs no installation at all.
Pulling the APK Onto the Device
Once the source passes your judgement, the 1xbet android application phone version file lands in your Downloads folder as a single package that Android can later verify line by line. Keep the page that offered it open in a tab, because a responsible source names the version it distributes and you may want that reference when an update prompt appears months from now.
A few habits cut most download-stage trouble:
- Use a stable Wi-Fi connection so the package arrives complete rather than truncated mid-transfer.
- Avoid parallel “mirror” tabs serving the same file at a different version – the newest build is the one support can actually troubleshoot.
- Let the download finish before tapping it, since a partial file triggers the cryptic “parse error” Android throws at corrupted packages.
- Rename nothing in the file name; tampered names are a classic hint that a middleman re-uploaded the package.
After transfer completes, a quick glance at the file size shown by your file manager against the size claimed on the source page closes this stage with something resembling evidence rather than hope.
What Android Actually Asks During Installation
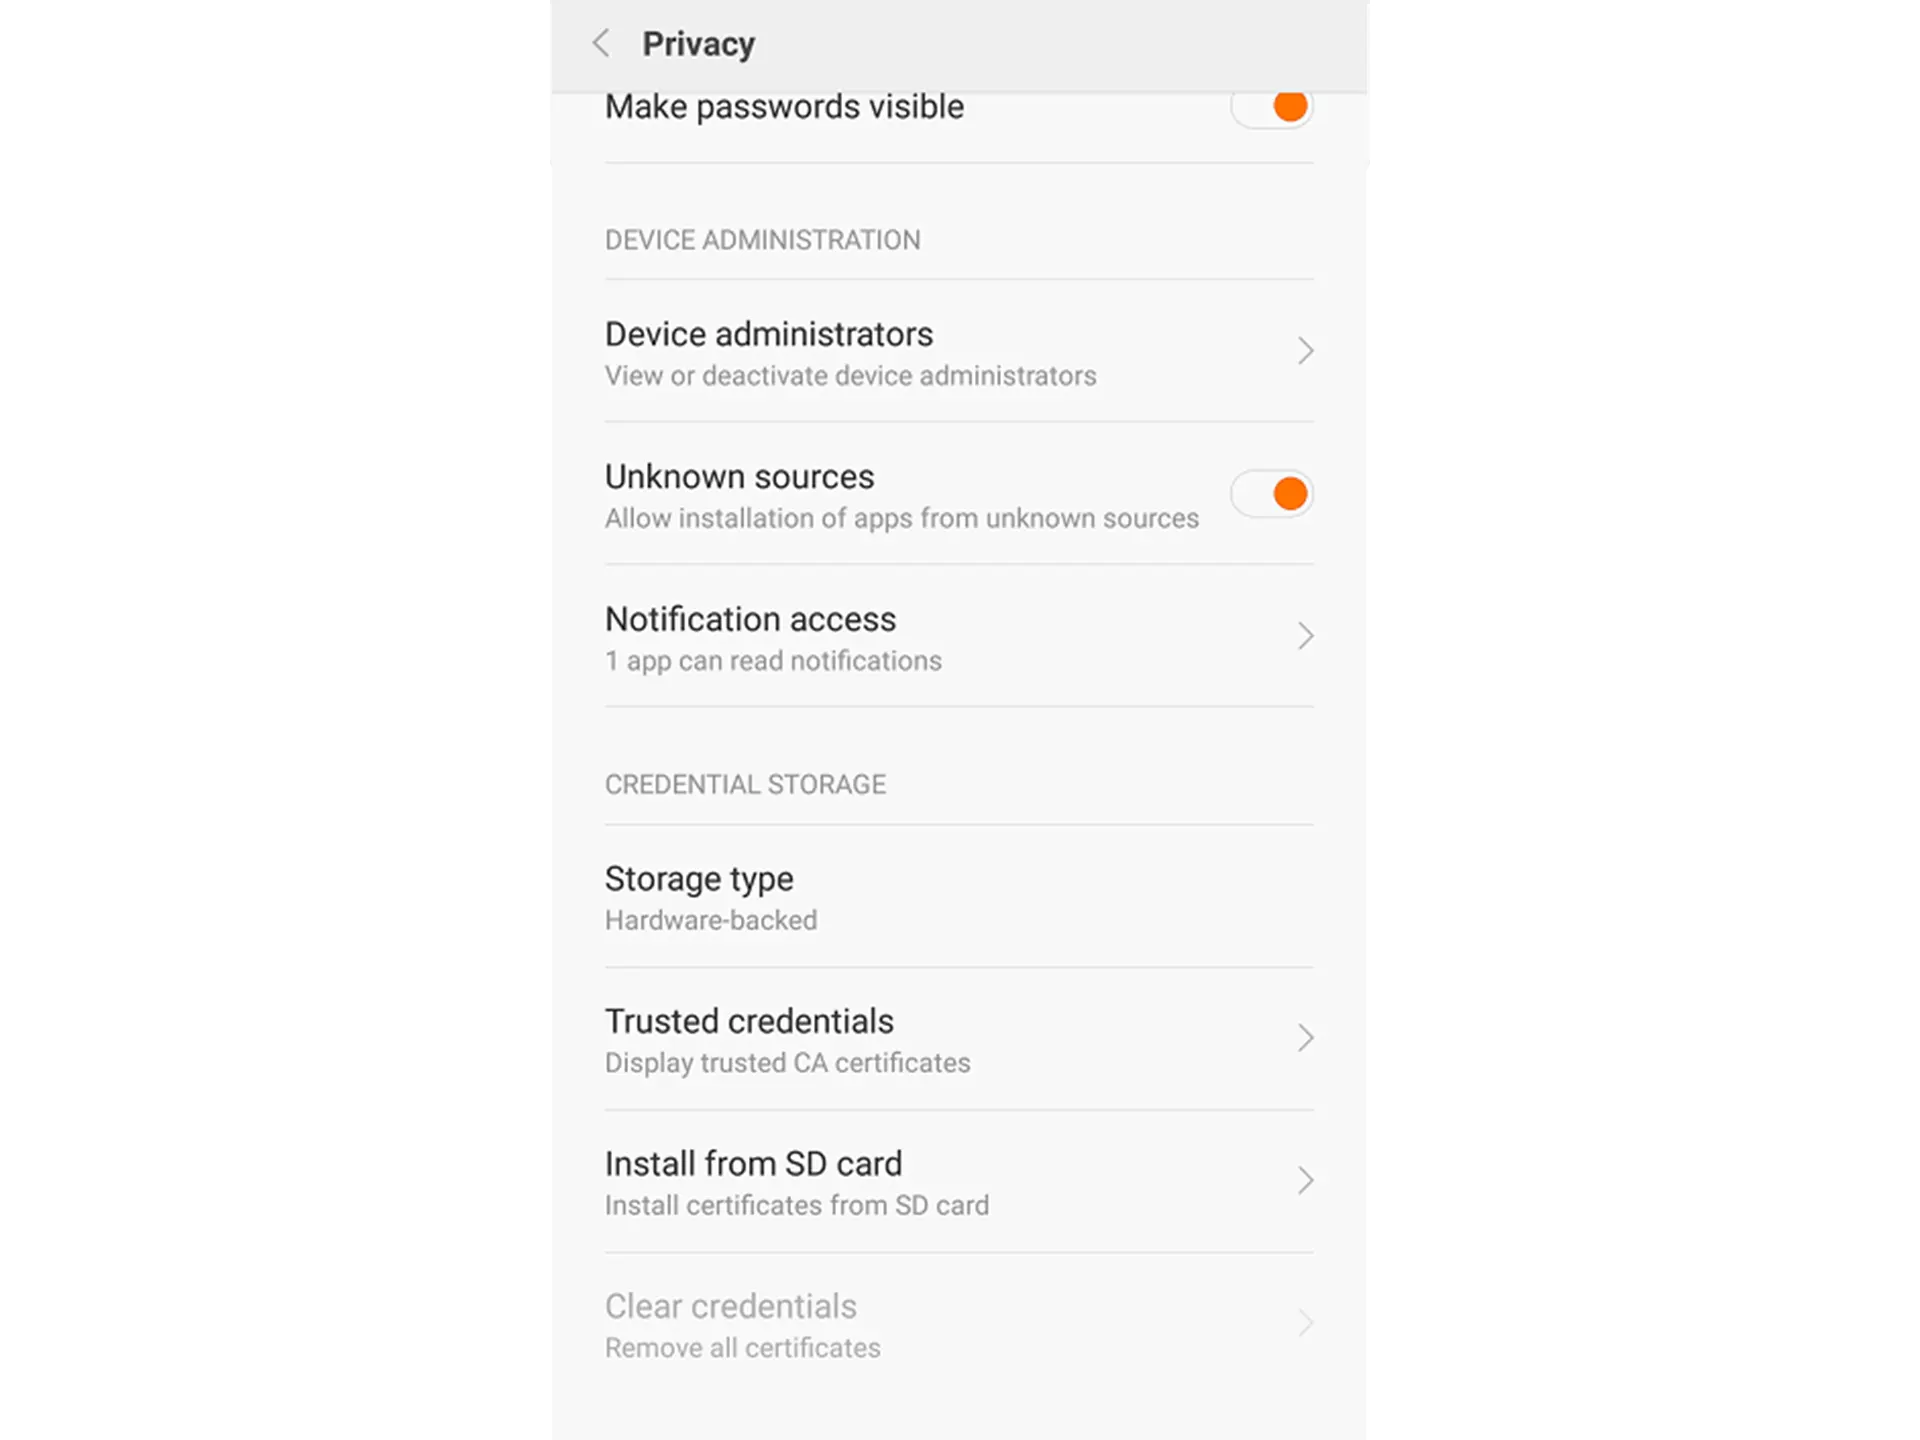
Tapping the APK starts a package installer that first requests one permission: allowing installs from unknown sources. Modern Android grants this per source app – the browser or file manager you opened the file with – not as a global switch, and you can revoke it right after installation finishes without affecting the already-installed app. The prompt exists because sideloading skips the store’s screening pipeline, so the system wants an explicit human decision for each origin.
Reading the permission screen in that light changes how the request list feels: Android is naming the door you’re opening, not accusing the file of mischief. Once the install completes, revoke the allowance for that source app under the Apps settings area, which narrows future exposure to deliberate choices only. The package itself still passes through signature checks – the system compares the developer’s certificate embedded in the APK with any previous install – and that comparison is why later mismatched-certificate updates fail rather than silently overwrite. Treat the permission dialog as a contract, and the rest of the flow – features, payments, account pages – sits on a foundation you chose on purpose.
Life Inside the App: Betting, Wallet and Updates
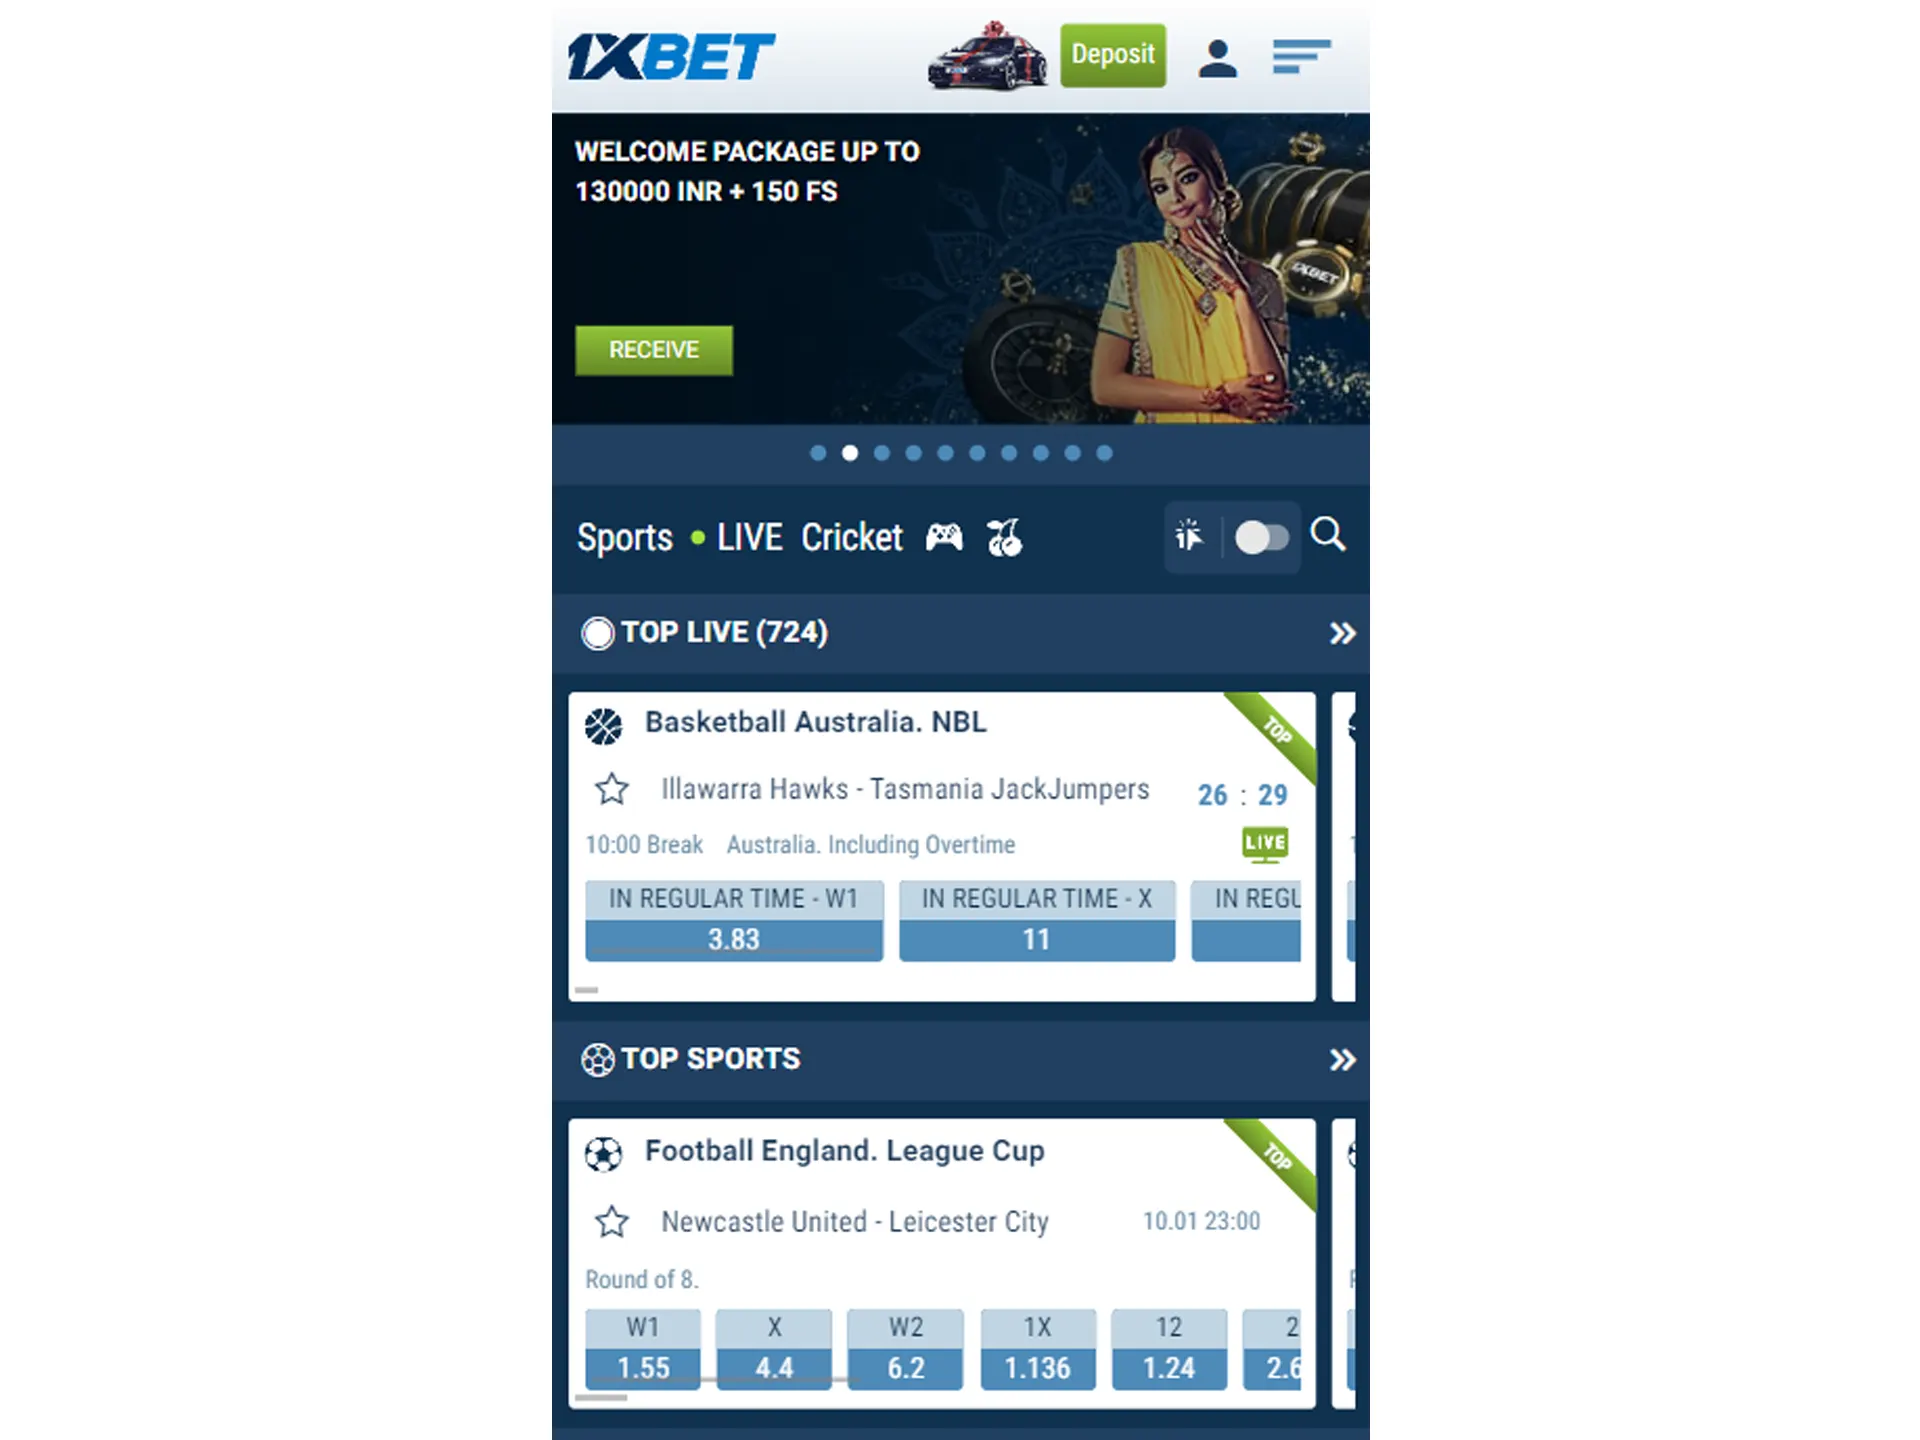
The installed client bundles pre-match and in-play markets alongside the casino lobby, cashier and account settings in one signed package whose layout varies by region and release. Live betting screens update odds without page reloads, deposits and withdrawals route through regional payment methods the cashier lists for your account, and the bet slip persists across sessions the way a browser tab cannot. Set a deposit limit inside the account menu on day one – gambling is leisure spending, never a revenue plan.
| Area | What the installed app adds over the mobile site |
|---|---|
| Sportsbook | Persistent bet slip, cached markets, push notifications for settled bets |
| Live betting | Streaming odds refresh without full page reloads |
| Casino lobby | Game libraries load once and stay local |
| Cashier | Saved payment paths under device-level lock |
| Account | Two-factor prompts and session history in one panel |
Updates arrive either in-app or as a fresh APK fetched from the same source. Android compares the signing certificate of the update with the installed build; a mismatch means someone re-signed the file, and the system refuses rather than merging them. Fix by uninstalling the old copy first – knowing local cached data goes with it – then installing the new build clean.
Reading Installation Errors Before They Intimidate
Package installer failures follow a small vocabulary, and each term points at a specific stage:
- Parse error – the package is truncated or corrupted; re-download over a stable connection.
- App not installed – often a signature mismatch with an older copy still on the device.
- Blocked by Play Protect – Google’s scanner flags unfamiliar sideloads; check your source judgement again rather than disabling blind.
- Insufficient storage – clear space so the installer can unpack, not just download.
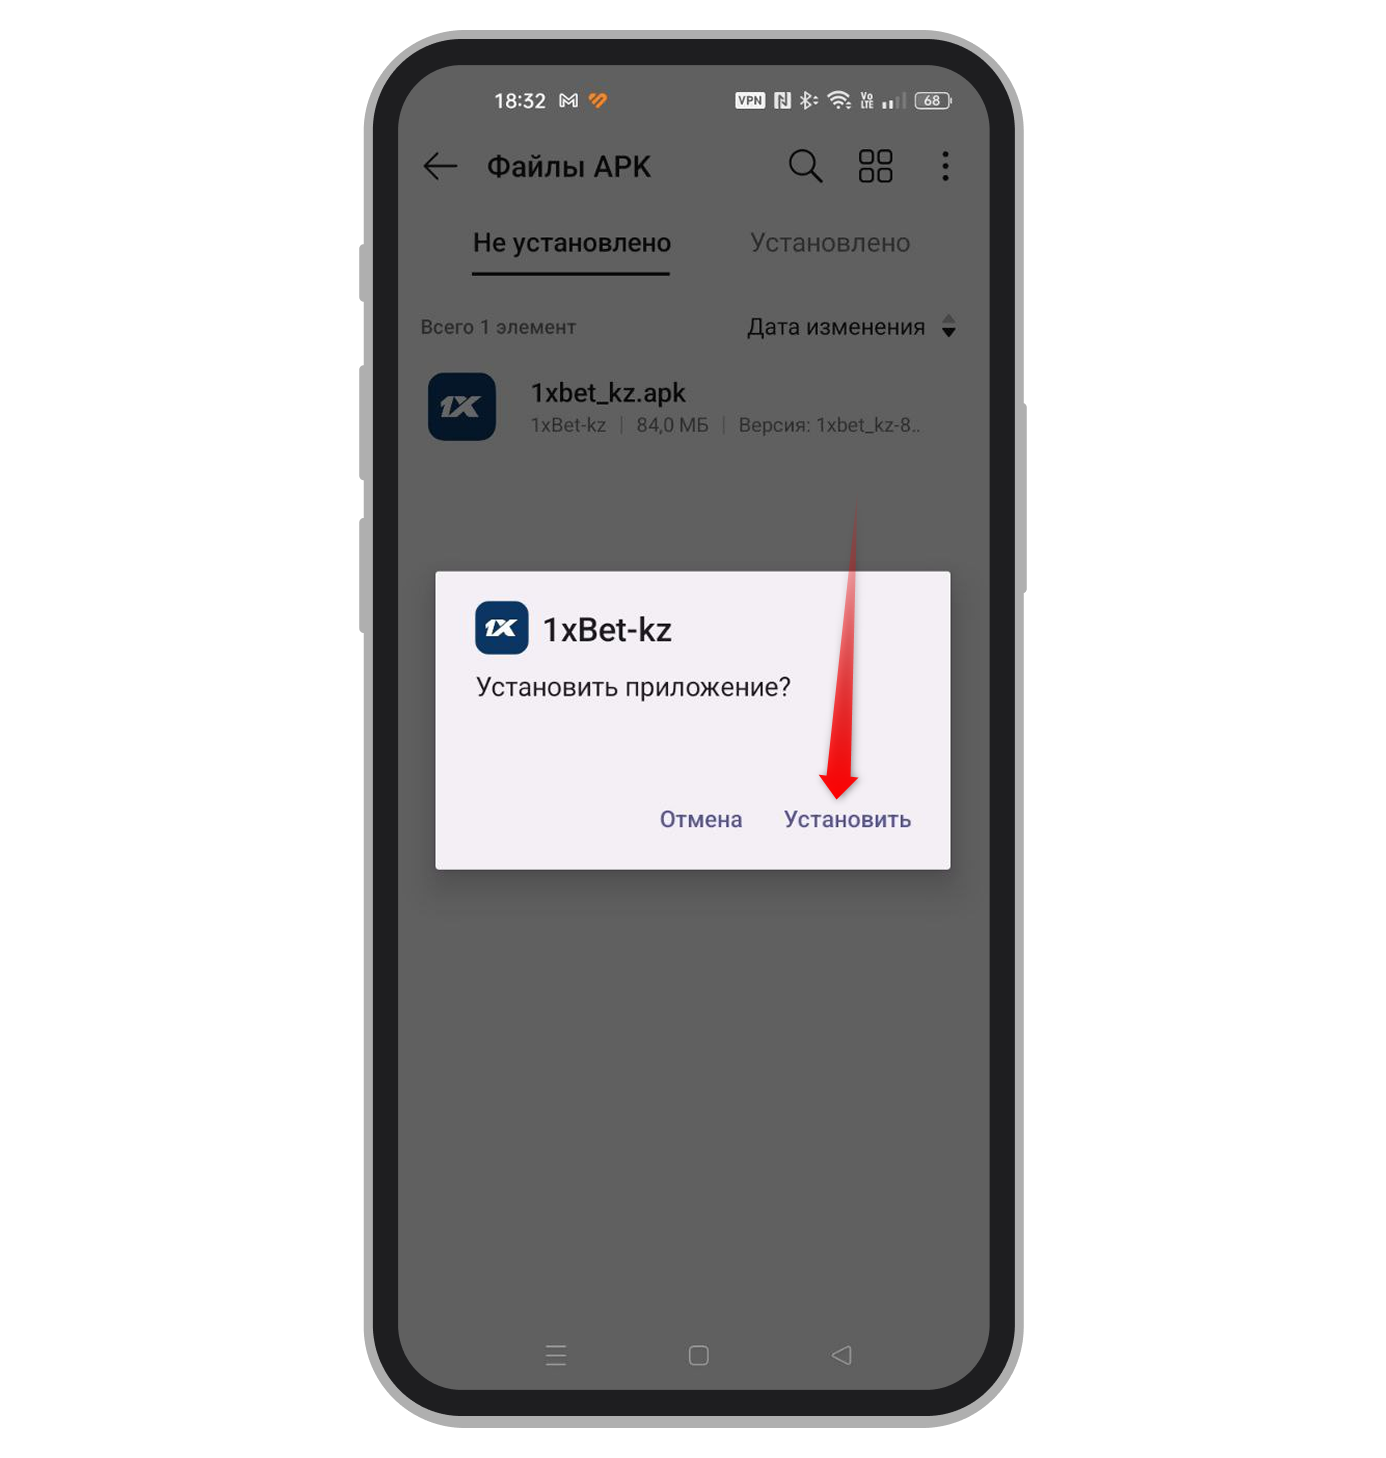
Behind every signing message sits code signing, the certificate mechanism Android uses to prove two builds come from the same developer, and grasping that turns the unknown-sources prompt back into the deliberate choice it was designed to be. Whenever an error feels genuinely ambiguous, the mobile website remains the fallback that needs none of this ceremony.
FAQ
Why does Android ask permission to install the 1xBet APK?
Because sideloading bypasses store screening, so the system demands an explicit yes for that one source app before proceeding.
Is it possible to disable the unknown-sources setting once installation is complete?
Yes, and you should – the app keeps working while future installs from that browser or file manager get blocked again.
What does “app not installed” mean with an APK update?
Usually a certificate mismatch between builds; only same-certificate updates are allowed to overwrite the existing copy.
Is checking the file size against the source page meaningful?
It catches truncated downloads and obvious tampering, though it complements rather than replaces judging the site itself.
Do I lose anything when uninstalling before a clean update?
Possibly cached local settings, since removal may clear app data – account funds and bets stay server-side regardless.